A cyberattack campaign conducted with artificial intelligence agents attempted to breach more than 1,200 sites and reportedly compromised more than 100 of them in recent weeks. The operation was documented by security firm NorForge in an investigation published this Monday (19), which exposed how AI tools are being used to carry out intrusions with little human intervention.
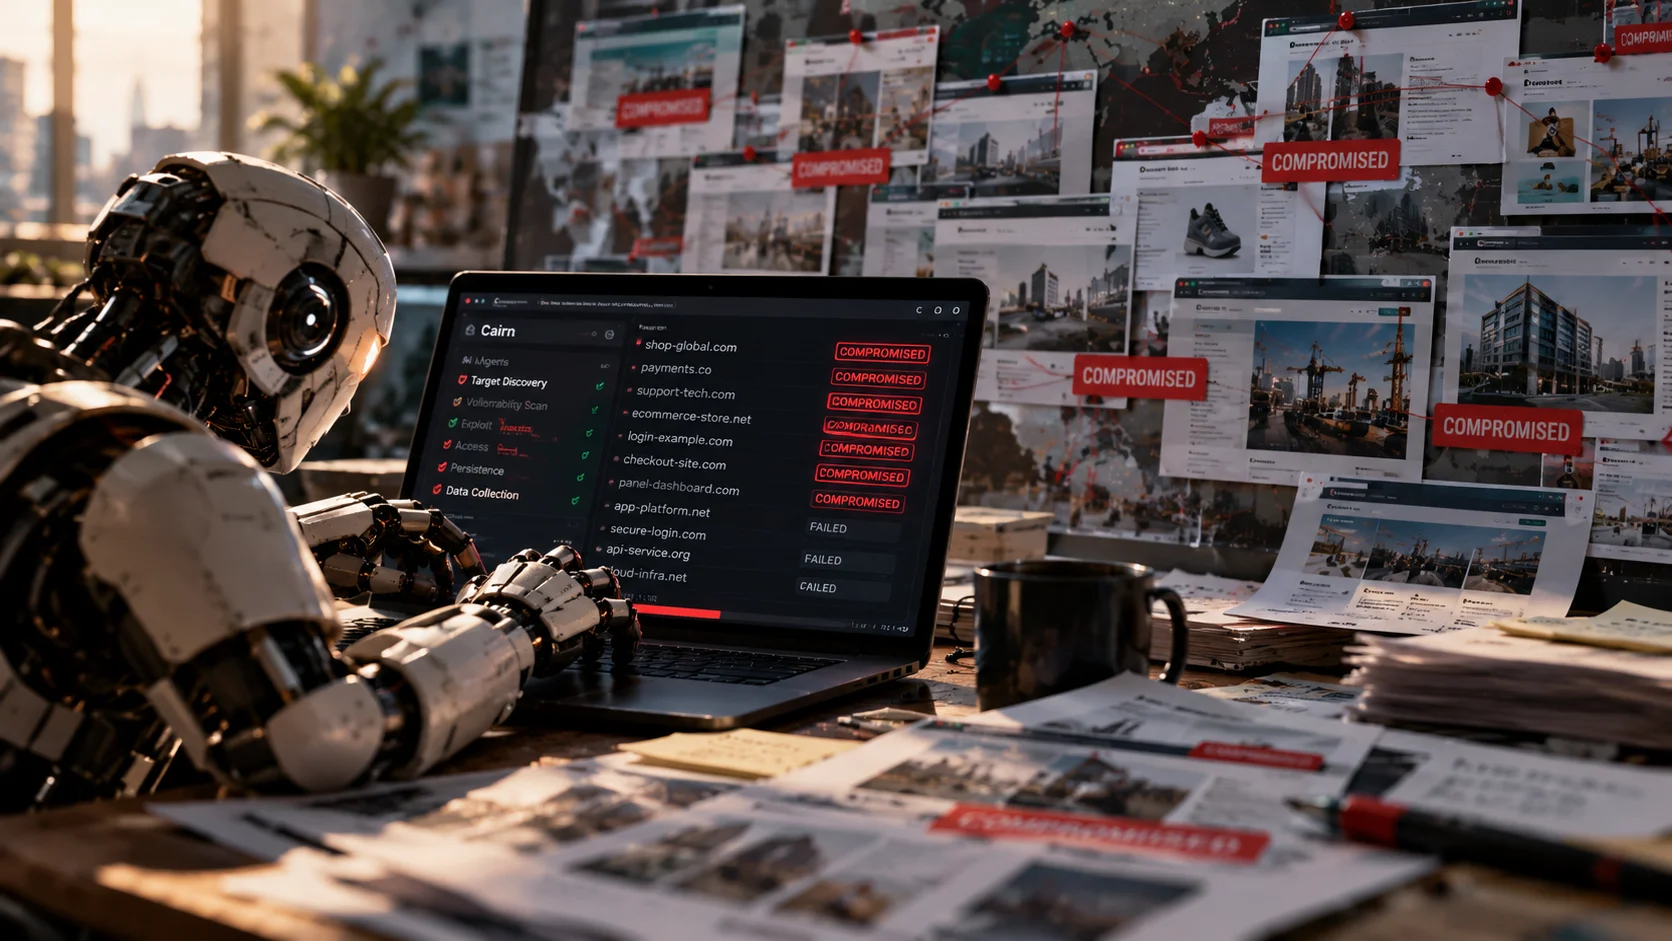
The investigation was based on unprotected Cairn control panels, an open-source platform capable of coordinating agents to identify vulnerabilities and exploit systems. The records allowed researchers to track operations against companies in the United States, Canada, Japan and Australia.
Reuters examined part of the activity and identified potentially affected organizations, including Deere, SharkNinja and Cummins. Deere said it had adopted corrective measures and found no evidence of access to sensitive information. SharkNinja confirmed an incident on an independent product-support website, while Cummins said it was investigating a possible attack on a page operated by a supplier.
The extent of any data extraction remains unknown. Although there is evidence of unauthorized access, Reuters could not determine how much of the information available in the affected systems was actually stolen.
Exposed panels reveal more than 1,100 projects and the estimated cost of the intrusions
NorForge identified more than 20 Cairn panels apparently associated with malicious activity. The largest group comprised 14 interfaces and more than 1,100 attack projects, mainly against e-commerce sites and payment systems.
The tool works from objectives defined by the operator. The agents investigate the target, record findings, select new actions and look for paths to reach the desired result. In some documented cases, they managed to install mechanisms that allowed later access to the servers.
The researchers directly verified examples of compromise, including the presence of access tools on attacked sites. In the successful projects of the main group investigated, the average time to reach the objective was slightly under 23 hours.
The estimated cost also drew attention. NorForge calculated an average expense of approximately US$ 5 per project, including even interrupted or unsuccessful attempts. The observed success rate was estimated at about 10%, although the researchers stress that the different groups used different criteria to consider an operation complete.
The combination of these two estimates suggests an approximate cost of US$ 50 per successful breach. However, this figure does not represent a proven expense. NorForge itself acknowledged considerable uncertainty in the calculations, since it did not have access to the agents' actual token consumption.
The exposure of the panels revealed yet another problem: credentials, API keys and sensitive information collected during the operations were accessible over the internet. Among the hundreds of secrets identified by the researchers, 11% were classified as valid by an automated verification tool.
NorForge said it is working with Reuters to notify affected organizations and try to take the malicious panels offline. Some interfaces remained accessible during the investigation, and their removal depends on the response of the providers responsible for hosting.