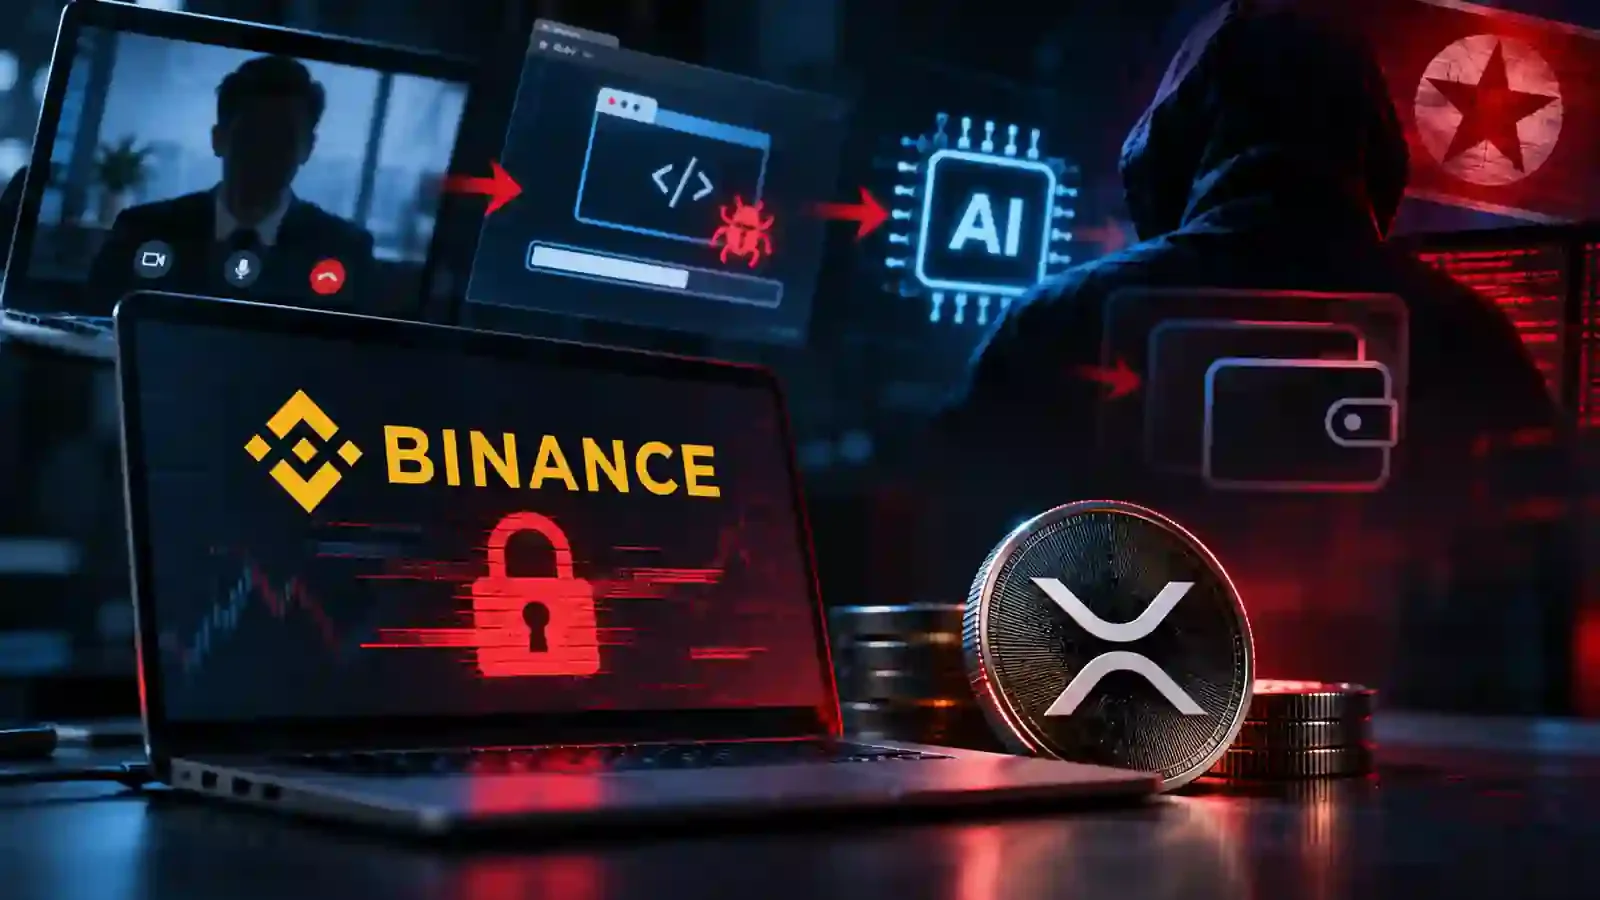
Binance released this Tuesday (3) an initial reconstruction of the attack that compromised approximately US$ 6.34 billion in cryptocurrencies on October 29. According to the exchange, the breach was prepared over months, began with a tampered software installer and a fake job interview, and advanced to the systems responsible for authorizing digital wallet transactions.
The report describes how the attackers reached the computers of three engineers, used an internal artificial intelligence tool to expand access and obtained credentials that allowed them to execute unauthorized operations.
The offensive culminated in the transfer of 233.46 million XRP from five hot wallets in just four minutes, followed by movements of other cryptocurrencies, including bitcoin, solana and ether. Hot wallets are those connected to the internet and used by platforms to move assets.
How access to the engineers led to Binance's wallets
The first stage identified occurred in June, when an engineer from the wallet infrastructure team installed a tampered version of Homebrew, a tool used to manage software, while trying to set up an AI coding assistant.
Binance says it detected the suspicious activity, replaced the device and renewed the associated credentials. Despite these measures, the attackers obtained information about the professional's role and that of his colleagues.
In September, another engineer was approached by an alleged recruiter on a legitimate job platform. The process included a video interview and a second conversation with someone who presented himself as the chief executive of a fictitious company.
During this stage, the employee received a programming task that required downloading a code repository. The material contained malicious software, executed during setup, that replaced a legitimate development component and established communication with a server controlled by the attackers.
Access was expanded on October 20, when the attackers used the compromised computer and an internal AI tool to reach the environments of two other engineers linked to the wallets. In this process, they discovered a token with permissions to deploy containers, environments used to run applications.
Nine days later, the criminals accessed the computer of one of these professionals, used the stolen credentials and deployed a container with a malicious script. The operation allowed them to reach Binance's internal transaction signing service.
Why withdrawals continued after the withdrawal suspension
On October 29, between 20:05 and 20:09 UTC, the attackers transferred the 233.46 million XRP. The exchange identified abnormal movements, started the investigation and adopted measures to suspend withdrawals and block assets.
The interruption, however, did not prevent all fraudulent transactions.
According to the report, the attackers used the Ethereum EIP-7702mechanism, which allows certain execution rights of an account to be delegated to smart contracts. After gaining improper access to the signing service, they created authorizations that allowed them to move assets outside the platform's conventional withdrawal infrastructure.
Binance explains that it had to develop a specific procedure to revoke these permissions. The response was made more difficult by the wallets' distributed signing architecture, which did not provide a single private key capable of immediately canceling the authorizations.
The last unauthorized transfer, of 2,961.9 ETH, was confirmed on the blockchain at 23:56 UTC, almost four hours after the first movements. The revocation of the malicious delegation from one of the wallets was completed at 00:10 UTC on October 30.
Binance reports blocking of US$ 2.85 billion and promises to cover losses
The company says that approximately US$ 2.85 billion were frozen or intercepted, a value subject to reconciliation and market fluctuations. The amount does not necessarily represent funds already returned to customers nor does it establish the definitive net loss.
Binance stated that it will absorb users' losses and has set aside resources greater than necessary to cover them. According to the exchange, as of October 31, 98% of the assets in affected tokens had already been replenished in its reserves, while the acquisition of the remaining assets was still ongoing.
The FBI attributed the attack to the TraderTraitor group, associated with North Korea. The North Korean government rejects the accusation. The attribution does not yet constitute a judicial conclusion on responsibility for the episode.
As part of its response, Binance said it had rebuilt the affected wallet systems and internal AI tool, replaced devices, revoked credentials and reinforced security controls.
The exchange also announced the hiring of independent experts to review the investigation and evaluate its protection measures. The conclusions released on November 3 remain preliminary and will still be subject to an external evaluation.