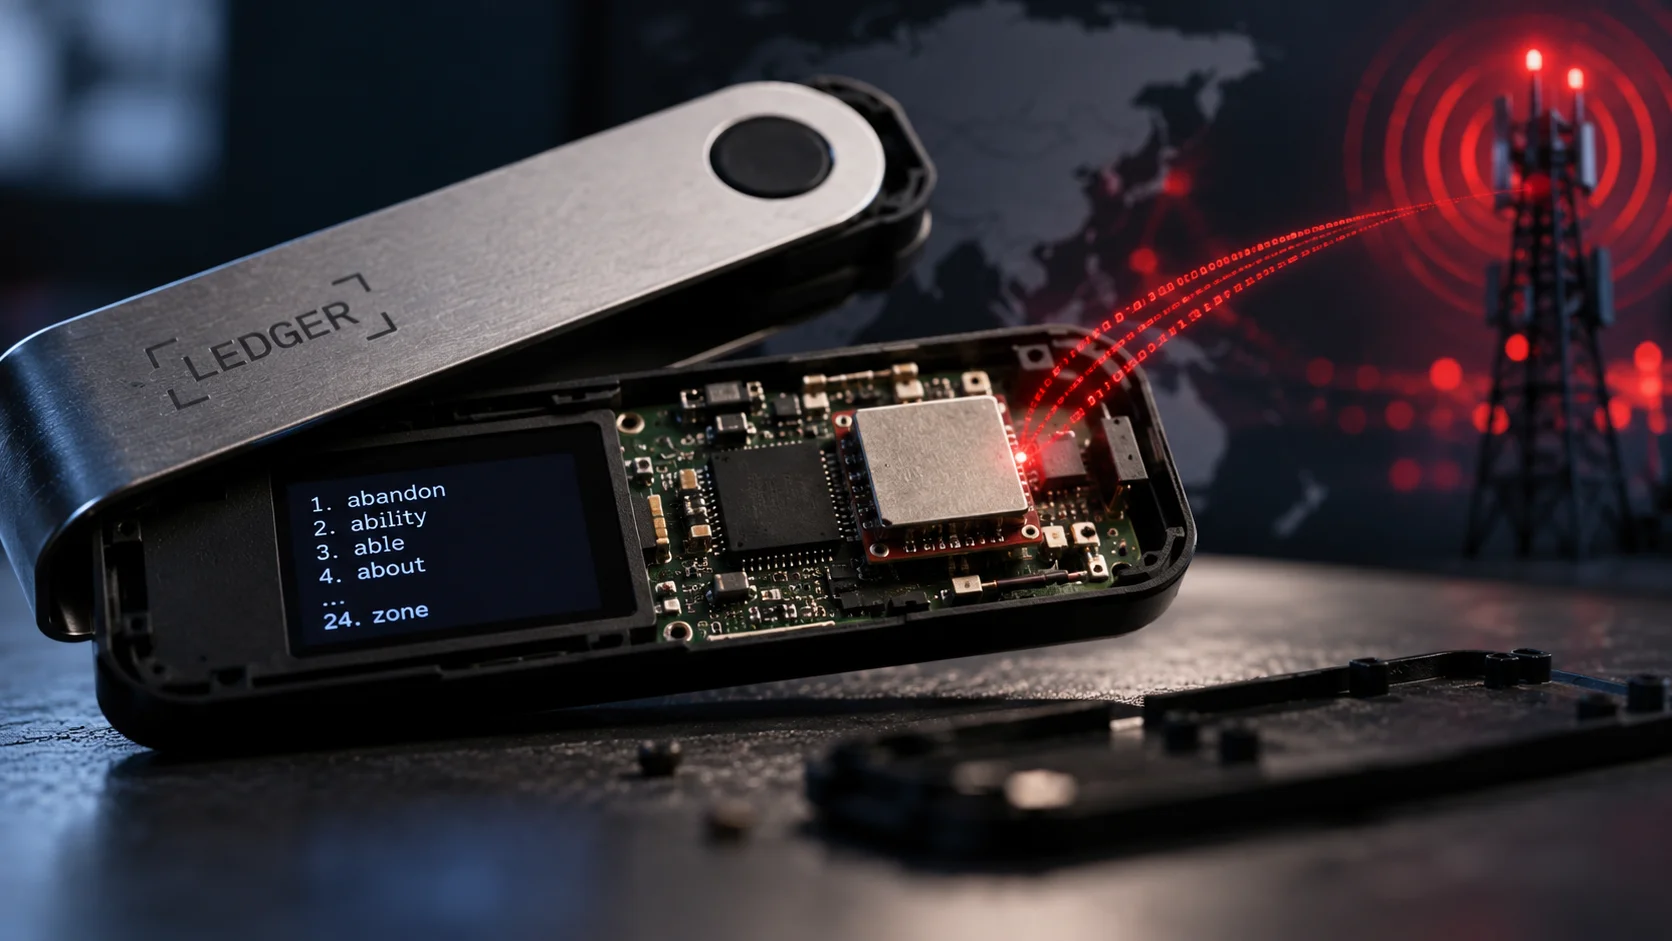
Ledger revealed on Tuesday (13) how tampered devices sold by reseller CryptoBilis, in Southeast Asia, managed to expose users' recovery phrases. An electronic component installed clandestinely in the wallets captured the 24 recovery words during setup and transmitted the data over the mobile network, allowing criminals to access the assets without needing the device.
The discovery is part of the investigation into cryptocurrency losses reported by CryptoBilis customers. The presence of a physical implant had been confirmed on October 10, but the update released by the Ledger Donjon security team detailed its operation.
The manufacturer states that all losses confirmed so far involve devices sold by CryptoBilis. The number of victims and the total amount stolen remain without official confirmation.
An additional chip copied the 24 words without modifying the security system
The implant identified by researchers used a microcontroller to recognize and decode the words displayed on the screen during the wallet's initial setup. It then transmitted the sequence over an LTE connection with eSIM, technology used in mobile phone networks.
The most relevant aspect is that the component worked independently of Ledger's protection mechanisms. According to the investigation, the Secure Element, the operating system and the transaction signing processes were not modified.
This means that a wallet could keep its security components intact and still have its recovery phrase compromised. With the 24 words, an attacker can restore the wallet on another device and move the funds without needing to alter the original device.
Ledger informed that it has not identified any compromise of its infrastructure, systems or services. The investigation continues to determine who made the modifications and at which stage of the distribution chain the devices were tampered with.
The case also triggered measures in European retail. MediaMarktSaturn suspended the sale of Ledger products in its stores and digital platforms after reports of tampering in Germany. The company treated the withdrawal as a preventive measure, while the manufacturer stated that there were no confirmed financial losses associated with the German case. Reports outside CryptoBilis remain under investigation and do not prove a widespread compromise of the devices.
For CryptoBilis buyers, the guidance is not to set up devices that have not yet been used. Anyone who has already initialized a wallet purchased from this reseller should transfer the assets to another device, using an entirely new recovery phrase. Simply replacing the device while keeping the same 24 words does not eliminate the risk if the original sequence has been intercepted.