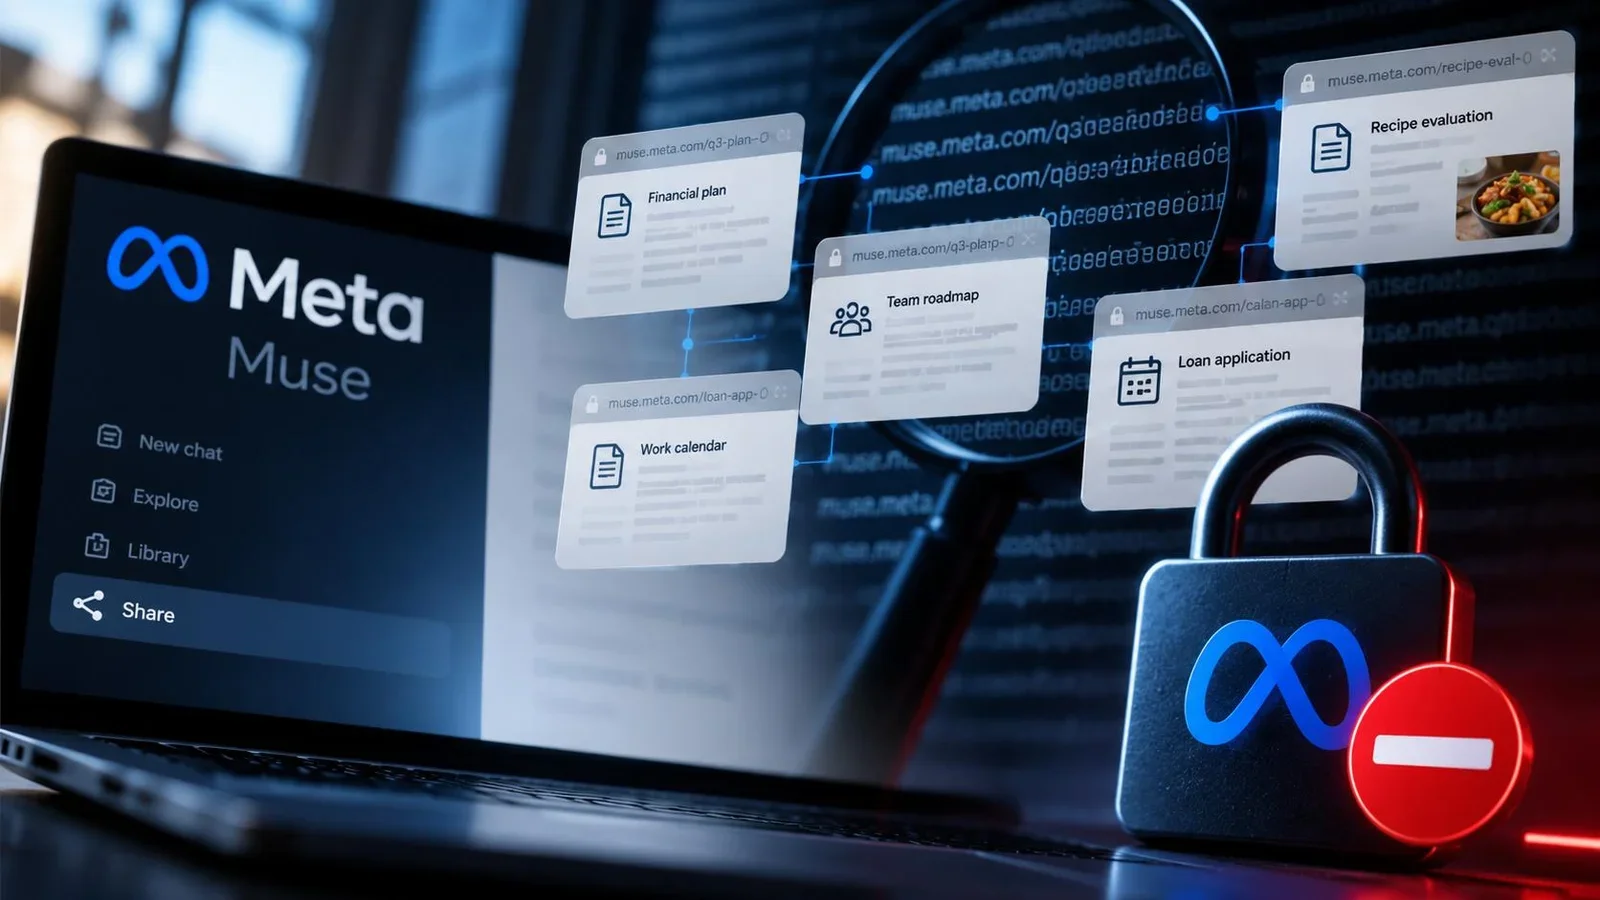
Meta suspended, on October 20, the conversation-sharing feature of the Muse artificial intelligence agent after researchers identified more than 6,800 addresses of shared pages in public DNS records. The discovery, made by the security company Claroc, showed that third parties could locate and access conversations without receiving the links from their authors.
The investigation, published on October 18, found personal and business documents among a few hundred pages examined. The materials included internal revenue assessments, loan applications, financial information and professional calendars. In one case, researchers found notes about a confidential meeting with representatives of an artificial intelligence laboratory.
The problem was not in the generation of the links themselves. Users had requested the sharing, but the way Muse built the addresses allowed people not authorized to receive them to discover their existence.
Tracy Clayton, a Muse spokesperson, confirmed to The Verge that Meta had halted the feature while it analyzed the report and considered changes to how those links could be found.
How DNS records made it possible to find shared conversations
Muse created addresses using the conversation title accompanied by a random identifier. This information appeared in the host name, the part of the address used by DNS systems to locate servers on the internet.
When someone opened a shared conversation, certain passive DNS services could log that host name and preserve it in searchable databases. Thus, the title and identifier that were supposed to make discovery of the content harder ended up available for lookup.
Claroc used one of these commercial services to search for addresses associated with Muse's sharing domain. After removing irrelevant records, it found more than 6,800 host names. Most of the pages examined did not contain sensitive information, but a portion contained documents that apparently had not been prepared for broad disclosure.
Blocking search engine indexing did not prevent discovery. Although Muse used instructions in the robots.txt file to discourage crawling of shared pages, that mechanism does not control DNS records or require authentication to open content.
The investigation also identified more than 75 records of shared pages in the public URL analysis service urlscan.io, demonstrating that the addresses could appear in other databases beyond the one used in the main research.
Claroc reported the problem to Meta on October 8, through its vulnerability reward program.
After the suspension, the researchers repeated access to 40 pages previously available without authentication. None of them opened again on October 20, indicating that the measure interrupted access to that sample.
However, the host names, including conversation titles, remained in passive DNS histories. Deactivating the pages does not mean that all records previously collected by external services have disappeared.
Claroc emphasized that the 6,800 addresses do not represent 6,800 confirmed exposures of sensitive information. The company examined only a sample and stated it had no evidence of malicious exploitation of the conversations.